XRP Healthcare announced its shutdown on September 10, 2026, after an attacker drained 4,011 wallets tied to the XRPH Wallet app, stealing an estimated $450,000 to $452,000 in XRP, XRPH, and related tokens in roughly three hours. According to reports from 99Bitcoins, the company made the difficult decision to wind down operations after nearly three years of building XRP Healthcare, which had been leading Ripple's charge into healthcare. The attack occurred on September 3, 2026, with the company first acknowledging the exploit on September 4 and confirming that XRPH, XRPHAI and other assets had been stolen from compromised XRPH Wallets. The breach originated in how XRPH Wallet generated credentials, with the application passing a 55-character value into xrpl.Wallet.fromEntropy(), a function that expects raw bytes. Only the first 16 characters were effectively retained, leaving 14 variable digits and reducing the possible input space to about 2^46 from the intended 2^128.
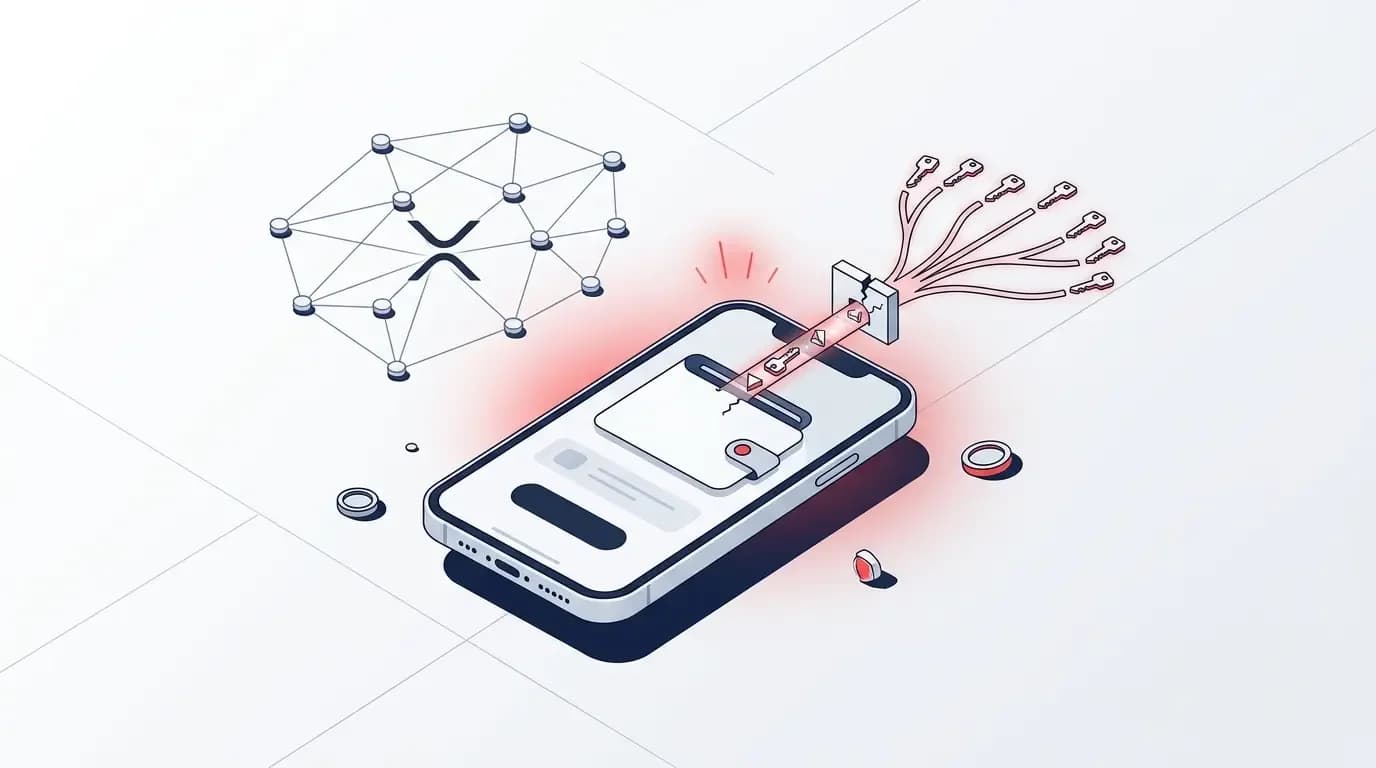
The root cause of the security breach traces back to June 13, 2023, when a defect was introduced into how the app generated wallets. As reported by 99Bitcoins, instead of feeding proper randomness into the XRP Ledger's key-generation function, the app passed in improperly formatted entropy. XRP Healthcare's development team described this as a defect where the app used a stamping machine that could only produce a few thousand distinct patterns, drastically shrinking the effective keyspace behind every wallet the app created. The company confirmed that the defect remained unpatched at the time of their September 8 technical report, with the key derivation process being deterministic and the underlying algorithm publicly readable. The developers also found use of Math.random(), which could have reduced the practical search space further. The team reproduced private keys for nine live wallets, including four confirmed drained accounts, using public information and a partial scan of the reduced keyspace.
According to on-chain analytics platform XRPL.to, between September 3 and 4, 10,281 payments from 4,011 sender wallets were traced, with 4,010 wallets classified as victims after one sender funded the collector account. As reported by 99Bitcoins, the stolen assets were traced through XRPL → NEAR Intents → Ethereum → Uniswap V4 → DAI, with approximately 445,198 DAI remaining in a single Ethereum address. XRP Healthcare confirmed on September 6 that it had traced the funds end-to-end and was coordinating with law enforcement to freeze the stolen funds, while asking affected users to submit loss reports via Etherscan. The company confirmed that approximately 267,664 XRP, 23.2 million XRPH tokens, and 2.43 million XRPHAI tokens were moved into the identified collector. XRP Healthcare emphasized that the attacker didn't need to break elliptic-curve cryptography, as the shrunk keyspace from bad randomness is a classical, brute-forceable problem that ordinary computers can solve.
On September 10, XRP Healthcare announced it was preparing to delist its tokens, including XRPH and XRPHAI, with individual exchanges expected to set withdrawal deadlines. The XRPH Wallet applications will remain offline while the company retains its intellectual property and global trademark portfolio. The shutdown follows a business already burdened by development costs, a prolonged crypto bear market, and an unsuccessful public-listing effort. The company has advised affected users to abandon credentials generated through XRPH Wallet and move any remaining assets using newly created keys. XRP Healthcare will continue working with exchanges, platforms, authorities, and other parties while preserving technical and transaction records connected to the incident. The incident represents a wallet-generation failure rather than a consensus failure, with every stolen transaction being a perfectly valid, properly signed payment from the XRP Ledger's perspective.