The National Bank of the Kyrgyz Republic (NBKR) and CertiK have established a comprehensive security cooperation framework through a Memorandum of Understanding signed on September 9, 2026, in Bishkek. According to reports, the agreement was signed by Sanzhar Abdygaziev, Member of the Board of the NBKR, and representatives of CertiK. The framework encompasses cybersecurity, formal verification, AML/CFT, operational resilience, supervision, and knowledge exchange across digital asset oversight and the Digital Som initiative.
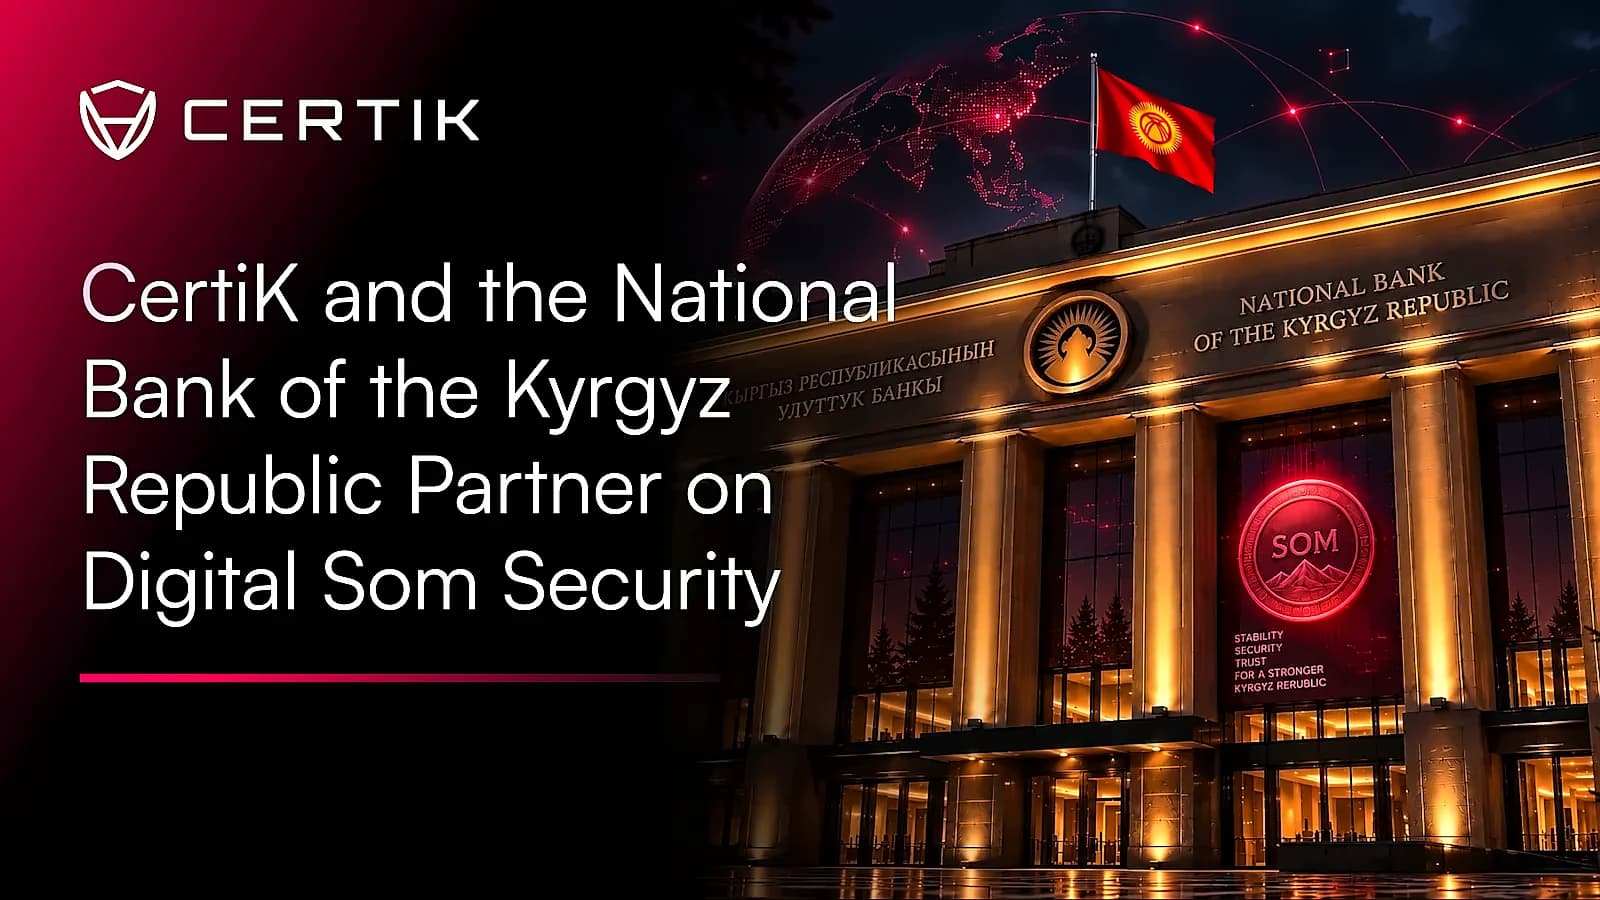
The partnership focuses on security assessments, formal verification, cybersecurity controls, and operational resilience measures during the development and testing of the Digital Som platform. As reported by CertiK, the company's Co-Founder and CEO Ronghui Gu emphasized that "Digital asset infrastructure requires security and risk management to be considered from the earliest stages of design through ongoing operation." The cooperation addresses operational resilience - the ability of digital financial infrastructure to continue operating and recover predictively following technical disruptions or cybersecurity incidents.
Beyond the Digital Som, the framework covers AML/CFT practices, transaction monitoring, digital asset custody, technical security standards, and licensing requirements. According to NBKR's Sanzhar Abdygaziev, the agreement establishes a framework for exchanging experience and expertise in blockchain and digital asset security, cybersecurity, AML/CFT, and the analysis and monitoring of digital asset transactions. The parties also plan to cooperate on analysis of risks and compliance trends associated with digital assets.
As part of the cooperation, the NBKR and CertiK will explore the potential use of CertiK's Supervision and Compliance solutions for ongoing risk monitoring and regulatory oversight. According to CertiK, their CertiK Compliance combines AML screening, fund tracing, threat intelligence, compliance reporting, and assessments related to assets and counterparties. The CertiK Supervision supports monitoring of virtual asset service providers, tokens, wallets, and transactions. Any deployment of these tools remains exploratory under the MoU and has not been announced as a contracted implementation.
The agreement addresses significant security challenges in the digital asset space, with Web3-related losses reaching $3.35 billion in 2025 and an additional $1.31 billion across 344 incidents during the first half of 2026, according to CertiK's Hack3D reports. Wallet compromise accounted for more than $444 million of losses during the first half of 2026, while code vulnerabilities accounted for $152 million. The MoU provides a framework for addressing security considerations including software integrity, key management, payment settlement, transaction monitoring, privacy, system availability, and operational resilience during CBDC development.