Cyber threats targeting India's banking and payments ecosystem are becoming increasingly sophisticated, with fraudsters now exploiting device compromise, token interception, weak backend validation and flaws in banking application logic to bypass security checks without directly breaching bank systems. According to the Digital Threat Report 2025-26 released by the Ministry of Electronics and Information Technology (Meity), Indian Computer Emergency Response Team (CERT-In), Computer Security Incident Response Team in Finance (CSIRT-Fin) and cybersecurity firm SISA, the rapid transformation of banking and financial services is creating a fundamentally new cyber threat landscape. The report warns that modern financial attacks are moving from direct compromise to trust-chain manipulation across biometric onboarding, partner apps, AI decisioning, real-time payments, APIs, programmable finance, and third-party ecosystems. The threat surface is no longer a perimeter but a distributed continuous shifting mesh of relationships across partners, platforms, models, APIs and infrastructure layers where none of which an institution fully owns or controls.
The Reserve Bank of India (RBI) has released a comprehensive discussion paper titled 'Exploring safeguards in digital payments to curb frauds' to address the growing cyber fraud crisis in India's digital payment system. According to The Economic Times, the central bank's most significant proposal includes a one-hour lag on large transactions above ₹10,000, which addresses the fact that 45% of reported fraud cases are above this threshold and account for roughly 98.5% of total value lost. The RBI has also proposed additional authentication for vulnerable users and scrutiny of mule accounts to curb fraud infrastructure. Other key measures include customer-induced controls and a kill switch to give users more transaction management capabilities. The Digital Threat Report 2025-26 notes that regulatory compliance frameworks are catching up, but they are catching up to an architecture that is itself still evolving, creating a lag between structural change and security model adaptation that sophisticated threat actors are actively exploiting.
India's digital payment fraud crisis has reached alarming proportions, with cyber fraud complaints and losses increasing significantly in recent years. As reported by The Economic Times, 24 lakh complaints were reported in 2025, up from 19 lakh in 2024 and 13 lakh in 2023. The reported value lost in cyber fraud in 2025 was nearly ₹22,000 crore, highlighting the scale of the problem. The rapid rise in digital payments has been accompanied by cyber fraud that has scaled alongside the convenience of digital payments, exposing vulnerabilities in the digital payment system's governance architecture. The Digital Threat Report 2025-26 warns that as digital services span multiple platforms, fragmented security and identity-based access increase risks, with a single compromised identity potentially enabling persistent, cross-platform access to multiple accounts and services.
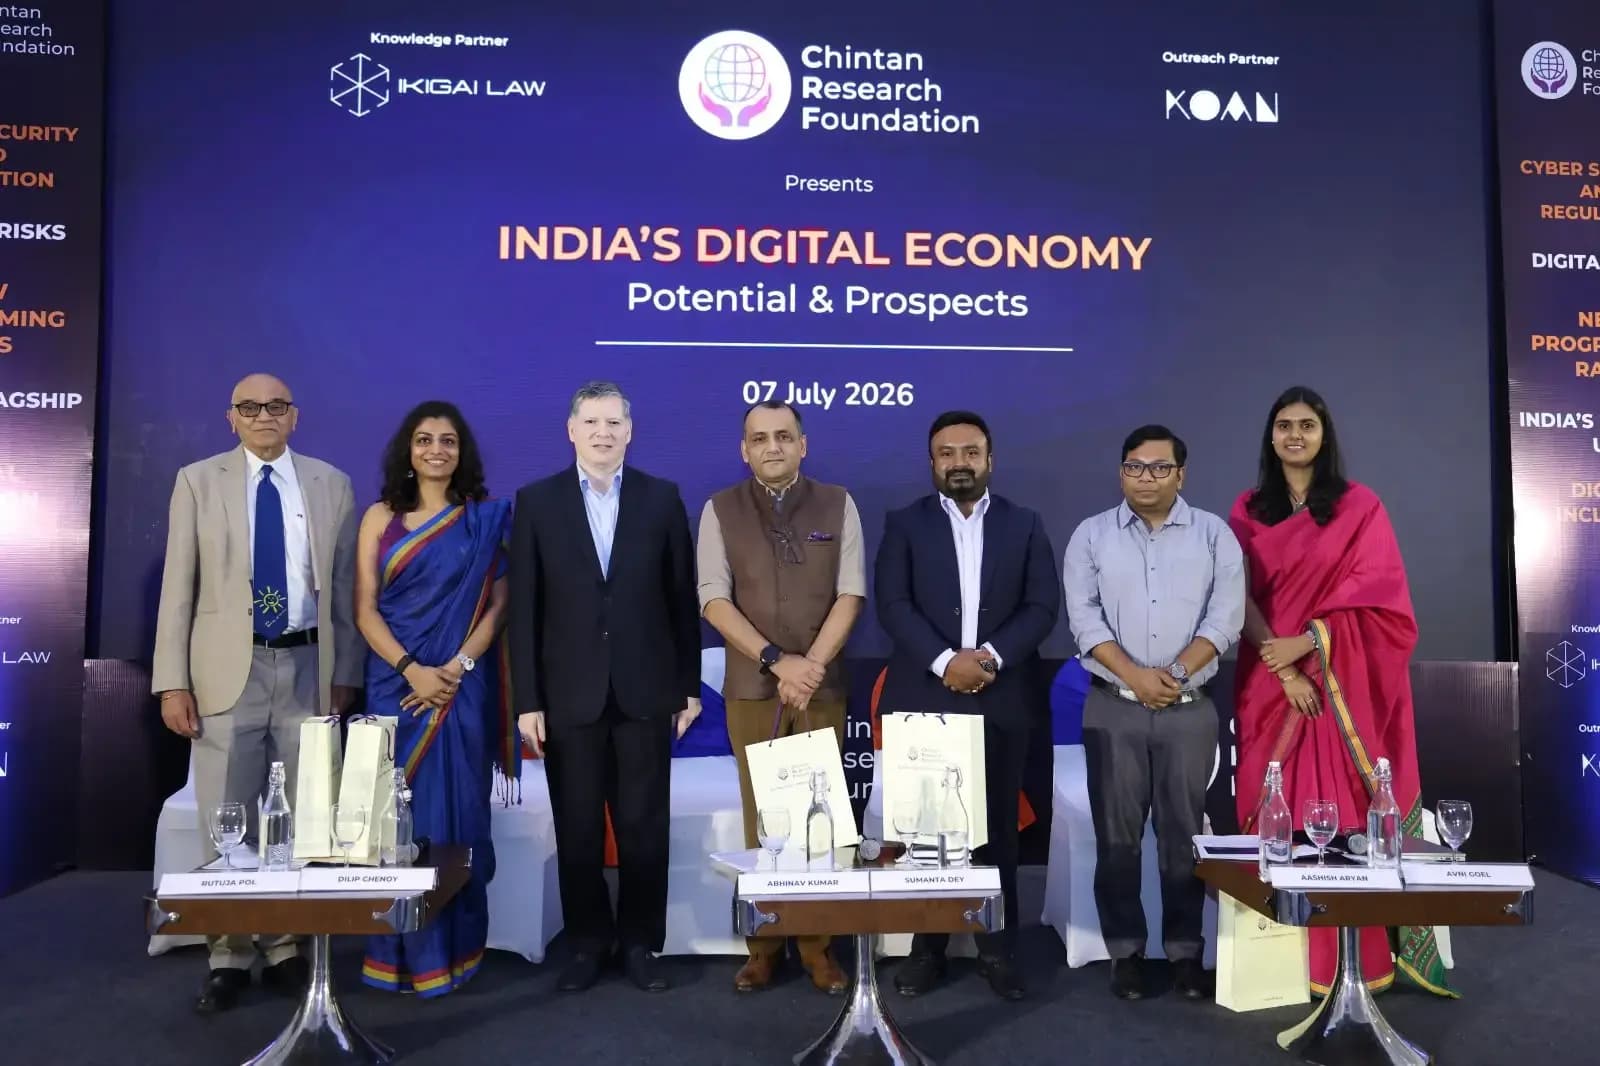
The Chintan Research Foundation (CRF) held a conclave on Digital Payments in New Delhi, bringing together policymakers, regulators, industry leaders, legal experts, technologists and researchers. According to reports from The Economic Times, the event was held in partnership with Ikigai Law and Koan Advisory Group to address emerging policy challenges and institutional frameworks required for India's rapidly evolving digital payment landscape. The conclave aimed to shape a secure and inclusive digital payments ecosystem, with discussions focusing on balancing innovation with trust and consumer protection.
While the RBI's proposals address critical fraud prevention gaps, several implementation challenges remain as cyber threats evolve faster than traditional security models. As noted by The Economic Times, the one-hour lag proposal risks understating the significance of low-value frauds, which constitute 55% of total reported cases. The additional authentication proposal for vulnerable users above 70 years and disabilities for APP transactions above ₹5,000 faces operational clarity issues regarding how banks identify vulnerable users and manage trusted person verification. The mule account restrictions require careful framework development to avoid delaying legitimate transactions while targeting fraud infrastructure. The latest threat report warns that compliance monitoring that relies on control signals becomes 'weaponisable' as attackers can suppress logs, manipulate alert thresholds, and maintain the appearance of a clean posture while operating inside a compromised environment. The convergence of real-time irreversibility, AI-driven decisioning, programmable financial logic, continuous identity planes, and ecosystem-dependent operations creates a threat environment where speed, complexity, and interdependency all compound simultaneously.